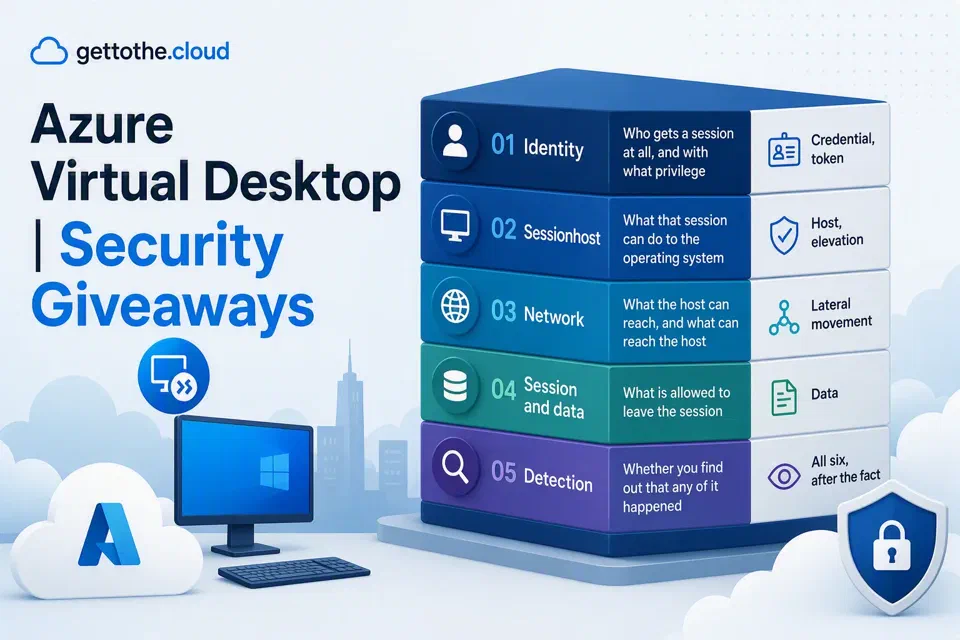
Azure Virtual Desktop | Security Give Aways
Part I of a three-part series on securing Azure Virtual Desktop. The trust boundary, the attack chain, and the takeaways worth acting on before you touch a single setting.
Tag
8 posts
Part I of a three-part series on securing Azure Virtual Desktop. The trust boundary, the attack chain, and the takeaways worth acting on before you touch a single setting.
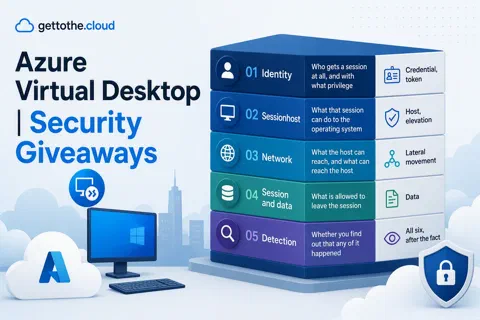
Part II of the AVD security series – closing the identity and operating system gaps, from RBAC and Conditional Access through Trusted Launch, local admin, Defender and the image pipeline.
Part III of the AVD security series – the network path, the session boundary, profile data protection, and building detection that somebody actually reads.
In this guide, we explore how to expand storage on your Azure Local home lab node and enable Scale-Out File Server (SOFS) for high availability. With SOFS, you can publish continuously available SMB …
Using Local security groups with AzureAD members which are attached to app masking assignment rules. Get those users from a CSV and add them to the local groups.
After the creating of the function app, we need to create the app masking rules and assignments. Create local groups and the rules to upload to the blob storage.
Create an Azure Function to get all members of application security groups and upload csv’s with UPN’s to Azure Blob Storage.
Using FSLogix AppMasking on Entra Joined Azure Virtual Desktop. Not supported, but hey there is a work around. Using Azure Function and some PowerShell, you can use AppMasking within Azure Virtual …
 Alex ter Neuzen