Azure Virtual Desktop | FSLogix App Masking with Entra Joined Devices III
 Alex ter Neuzen
Now we have exported all the users in the specific app groups to a blob container. We need to create also FSLogix App Masking rules and Assignments. We use the FSLogixRulesEditor for this. It can be found in the download of the latest agent.
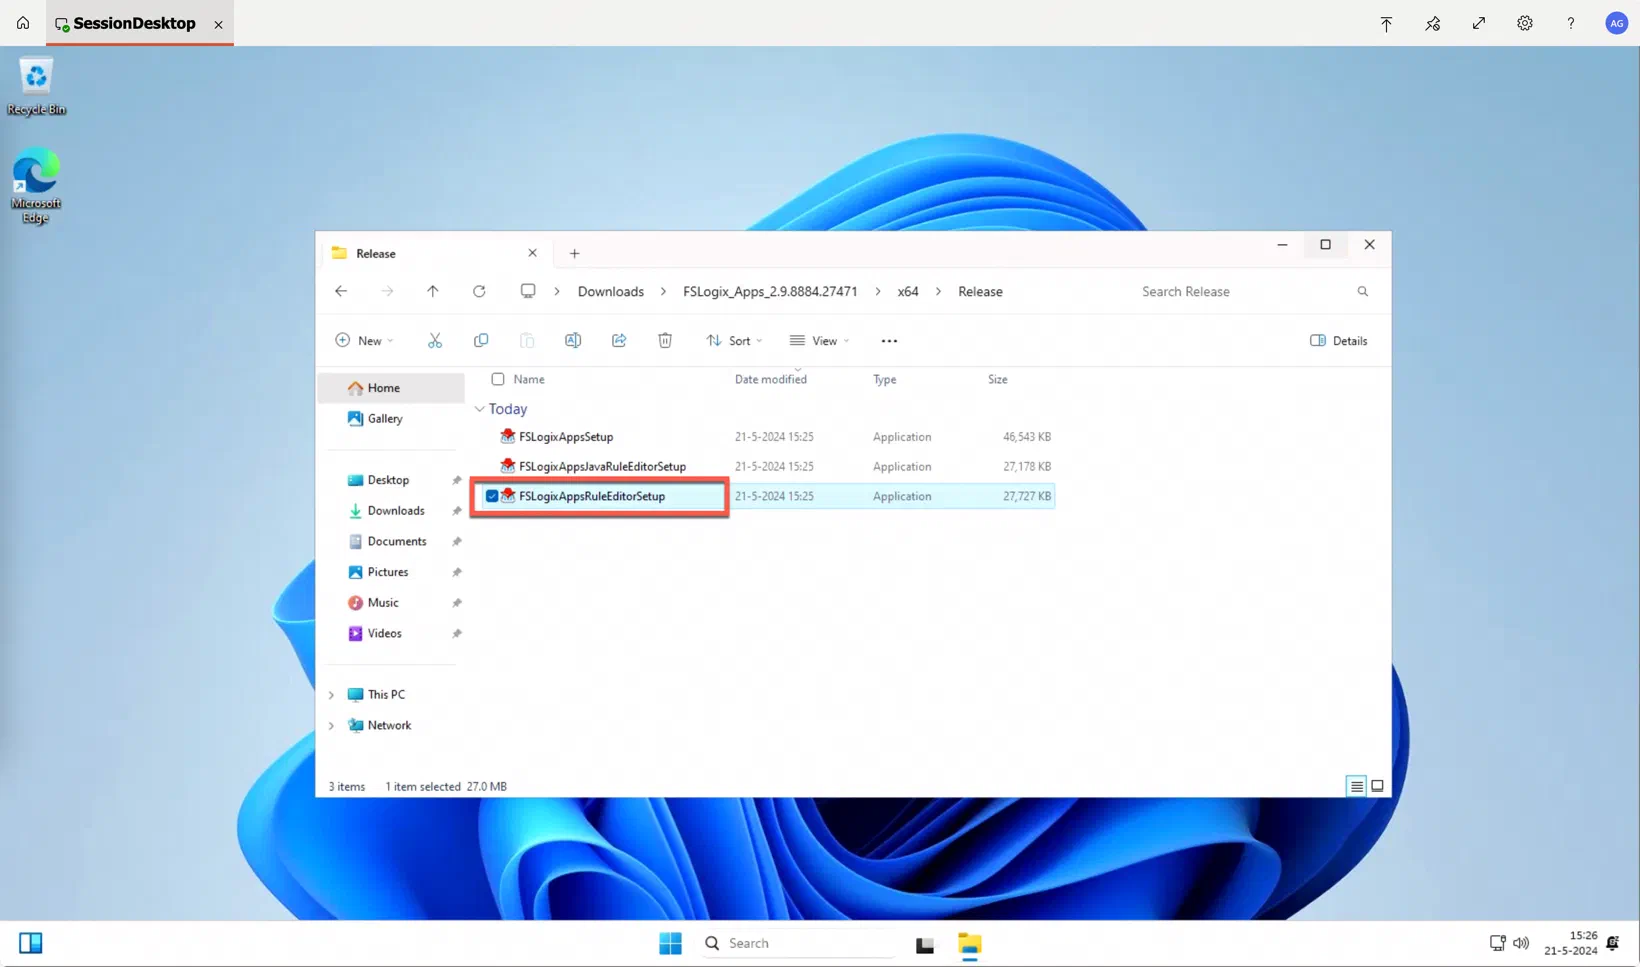
Using (link) will create the app masking rules and sets. But we are using local groups. So let’s do this with some random applications.
Local groups#
To create the correct app masking assignments, we need to create the local groups first that are defined in the function app. For this demo we create:
- app_group1
- app_group2
- app_group3
Those groups will be empty on this machine where we create the app masking assignments and rules.
App masking rules and sets#
After installing the FSLogix App Masking rules application you can start it from the Start Menu
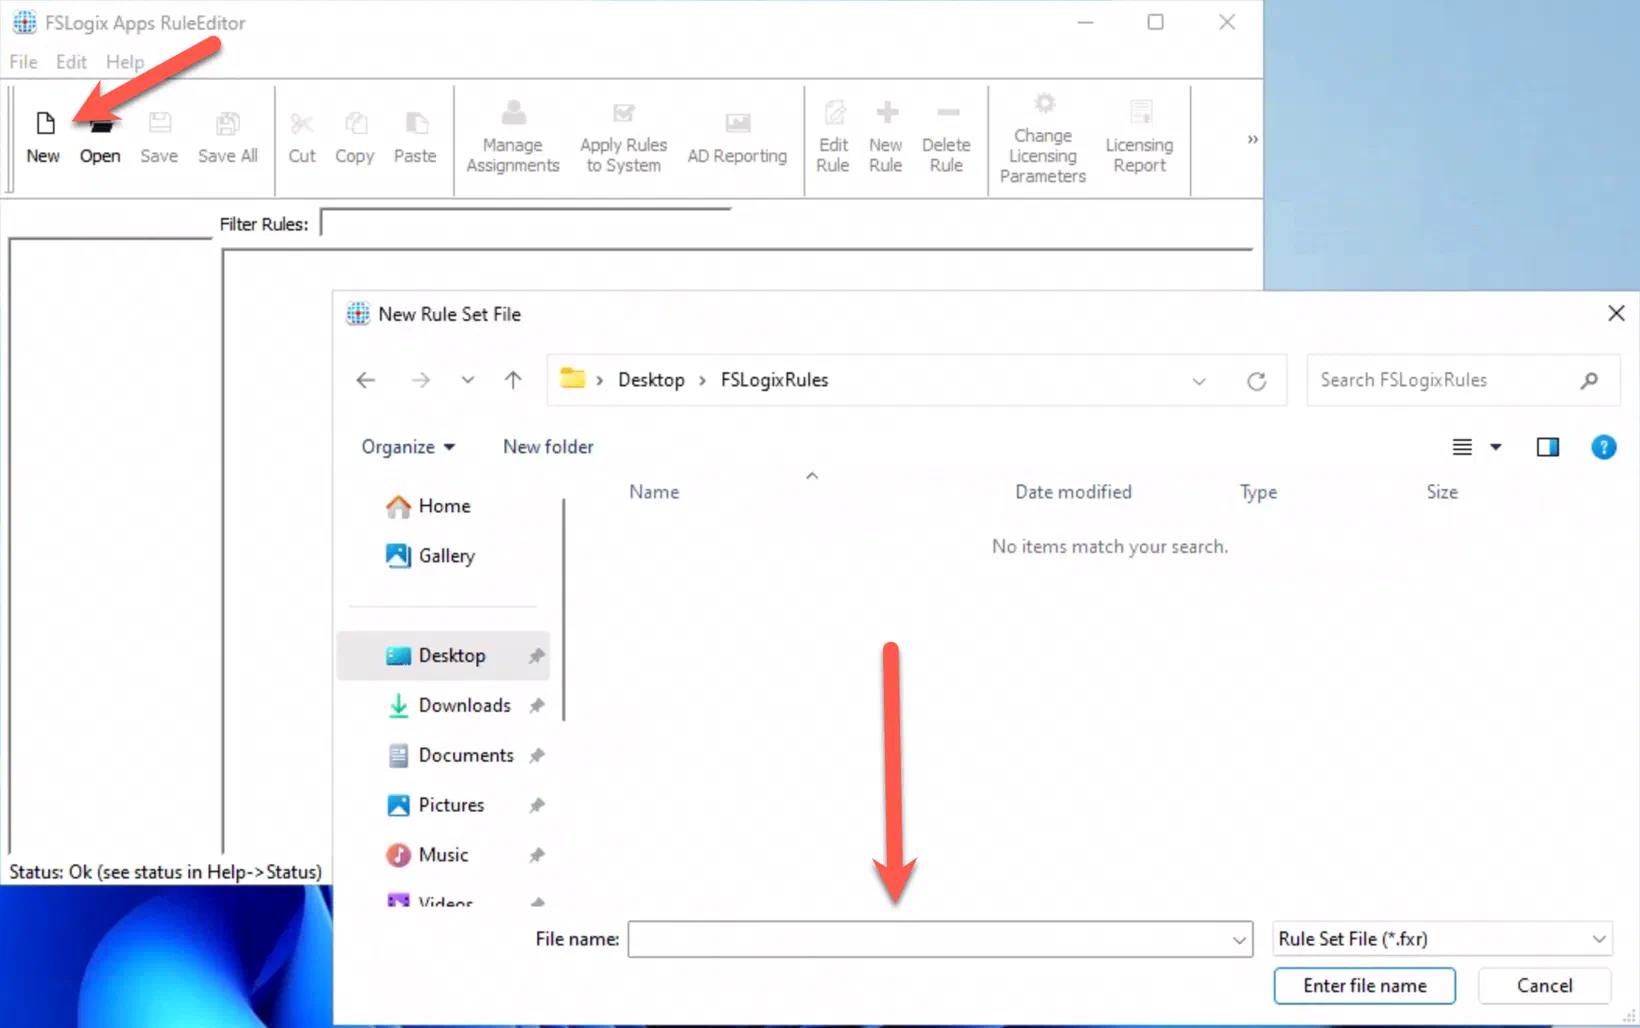
For this demo we locate the files in a folder on the desktop called FSLogixRules
Notepad
We will create a rule for Notepad.exe to hide from start menu with app group app_group1. For this we start with a blank rule.
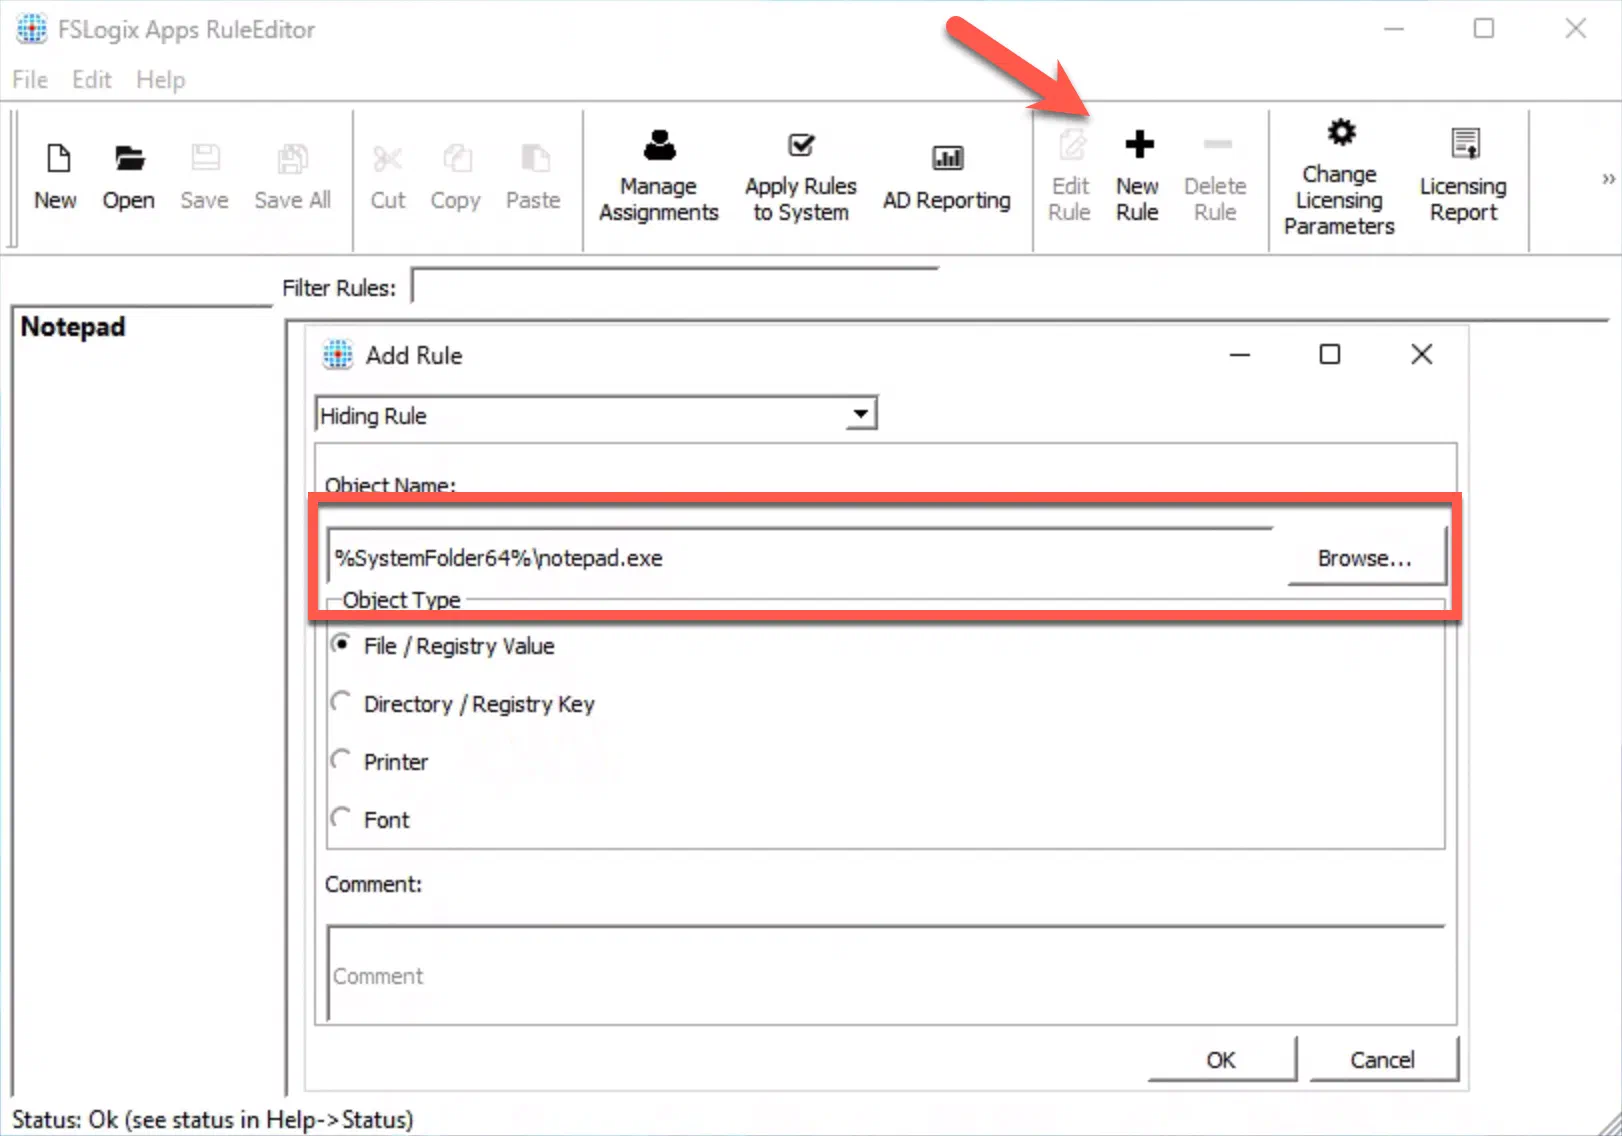
Select New Rule and browse to the location of the executable.
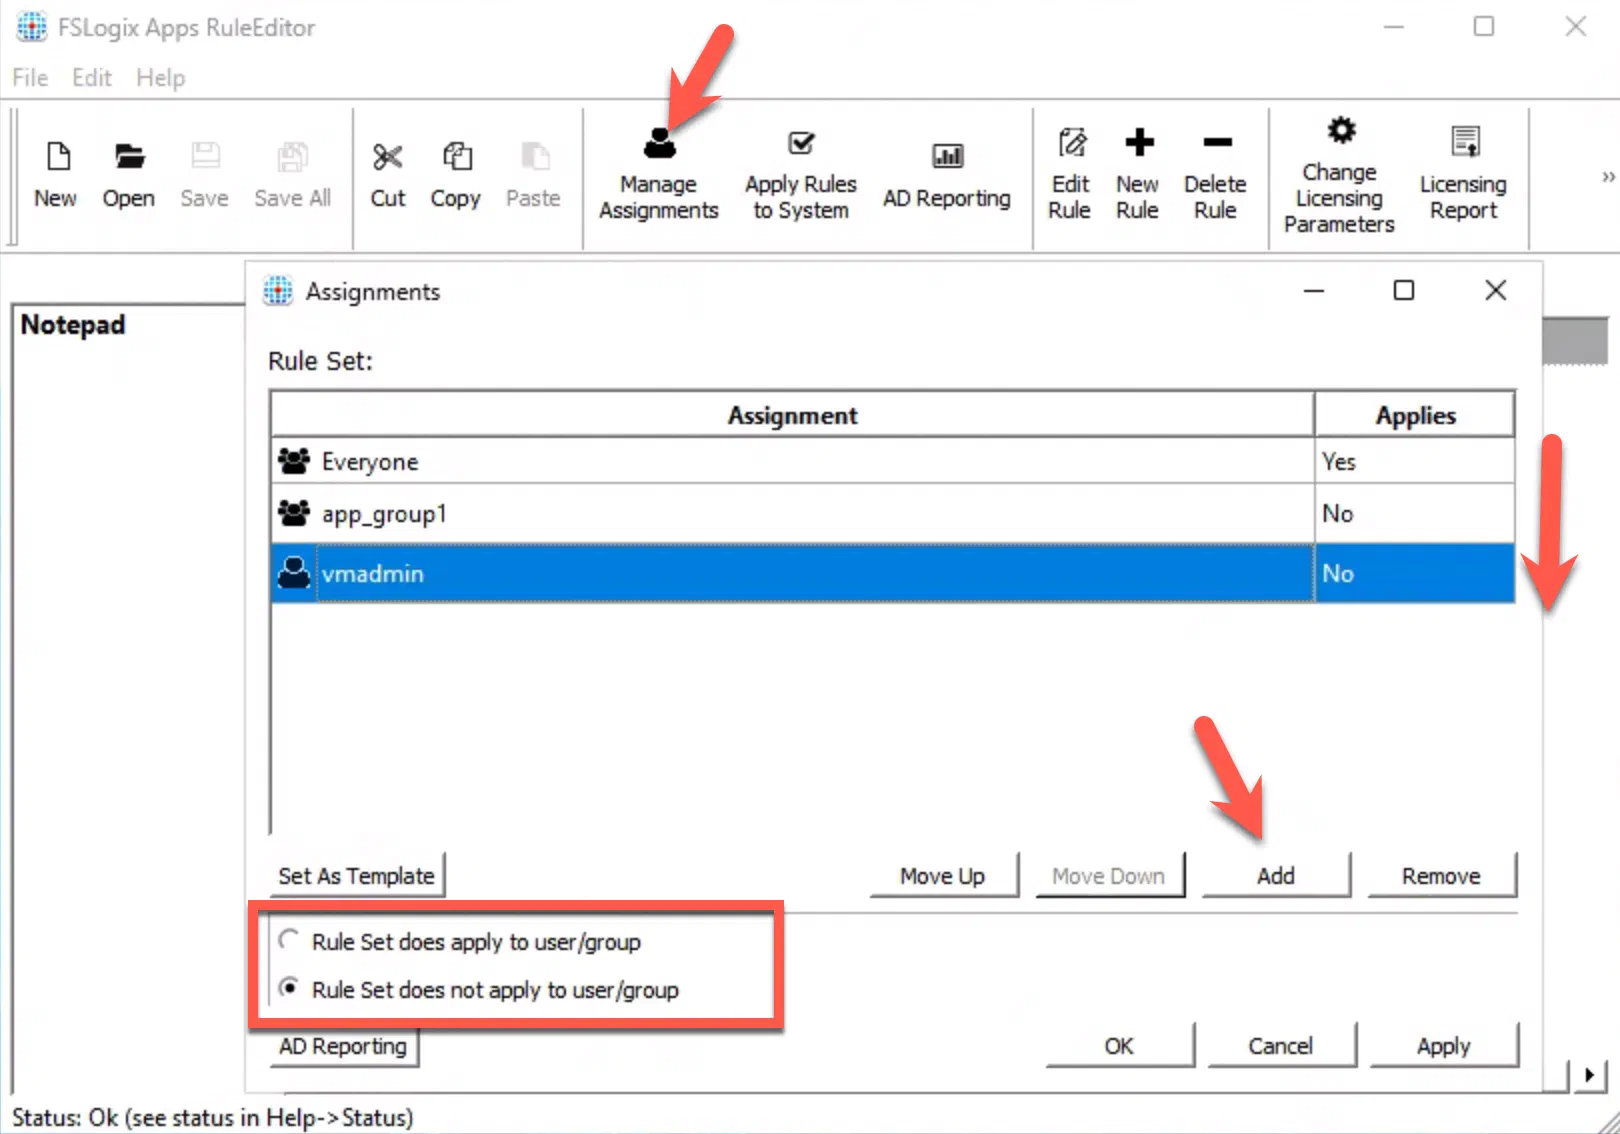
Add the users which the must be applied to. In this case we state:
The hiding rule is applied to Everyone unless you are in the app group app_group1 or you are user vmadmin. The rules are always working from top to down. Selecting the group or user will provide you the option if the rule must applied to that user/group or not. Click OK and Save.
Microsoft Edge
Creating a new rule for Microsoft Edge.
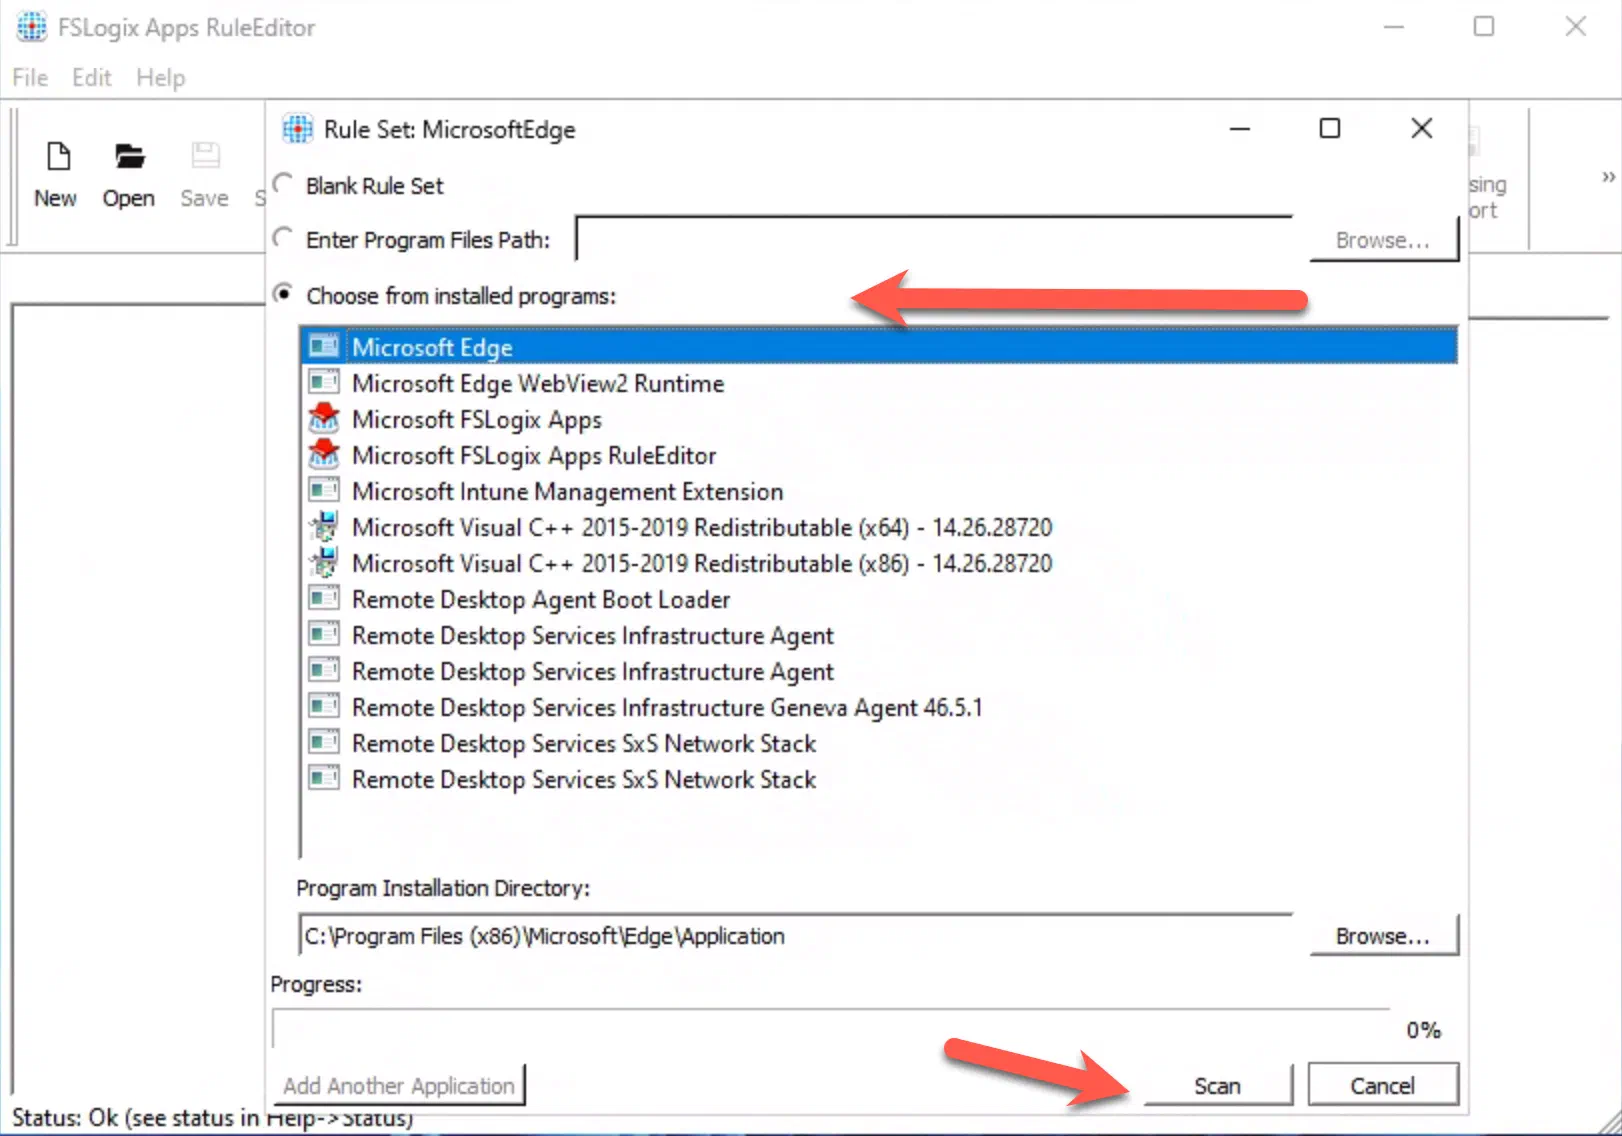
Use the Choose from installed programs the Microsoft Edge. Use the SCAN button to get all associated files and registry keys.
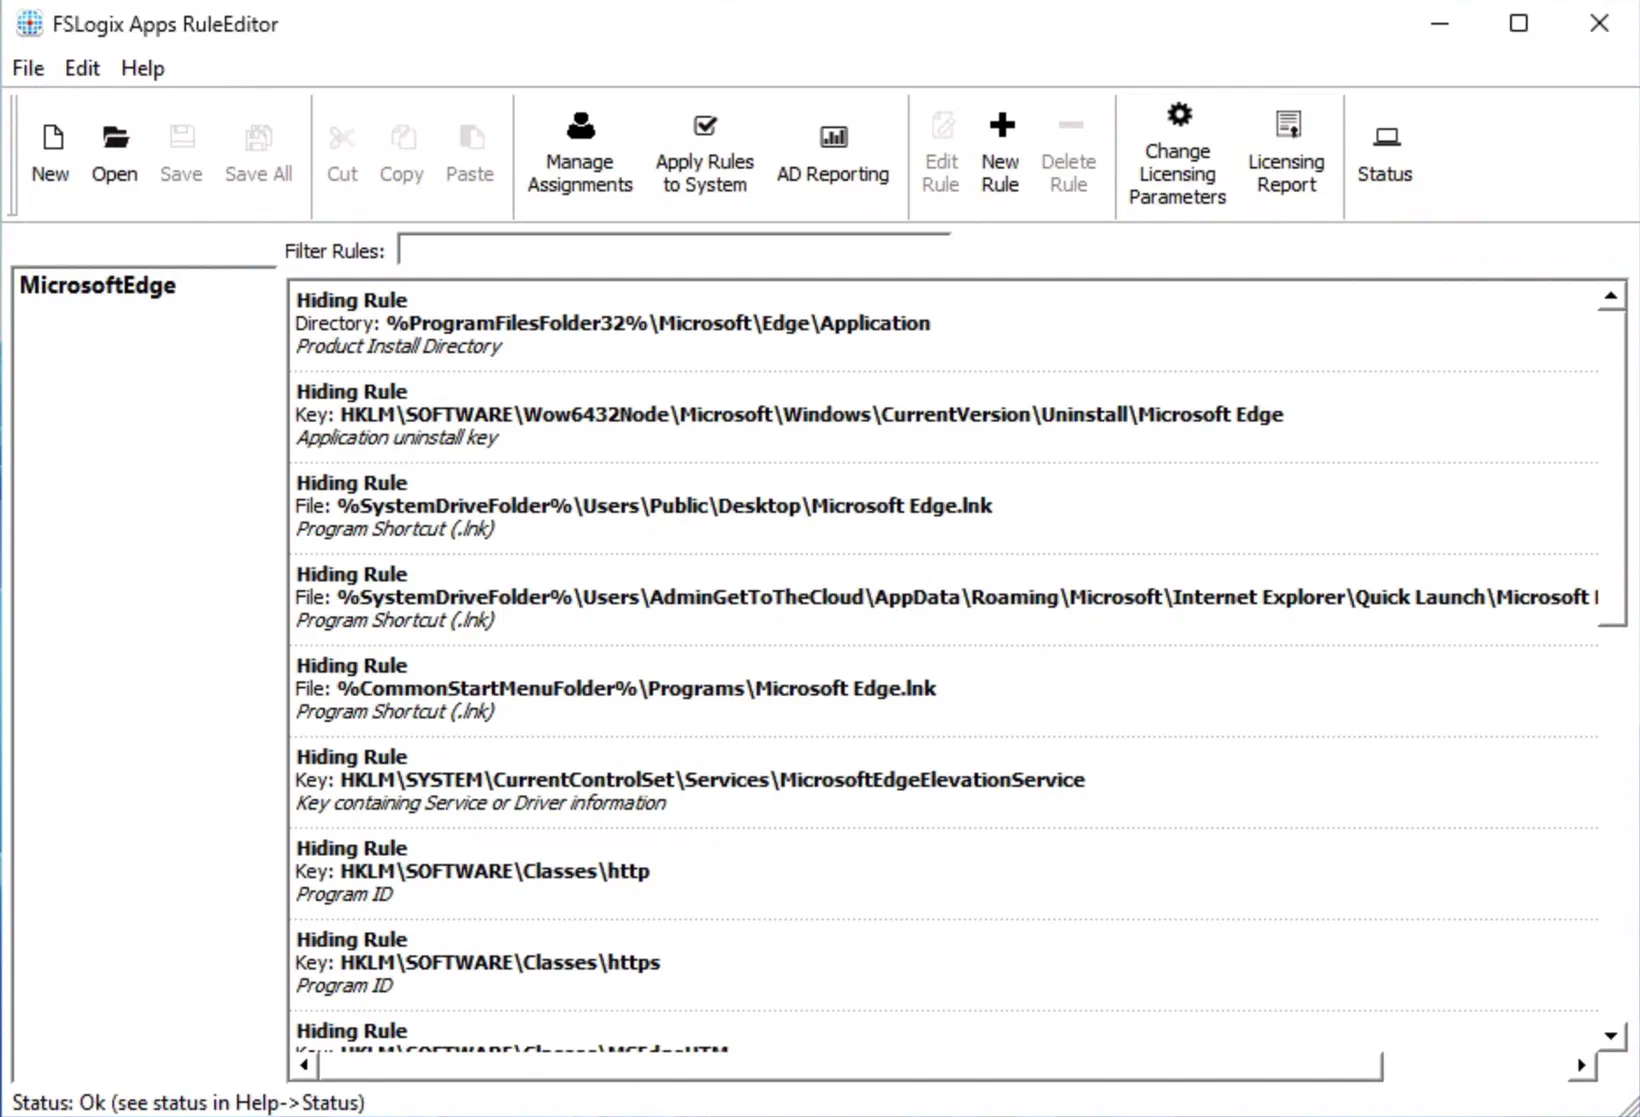
When everything is captured, you can edit the rules to what you need. The assignment can be done like the same as with Notepad.
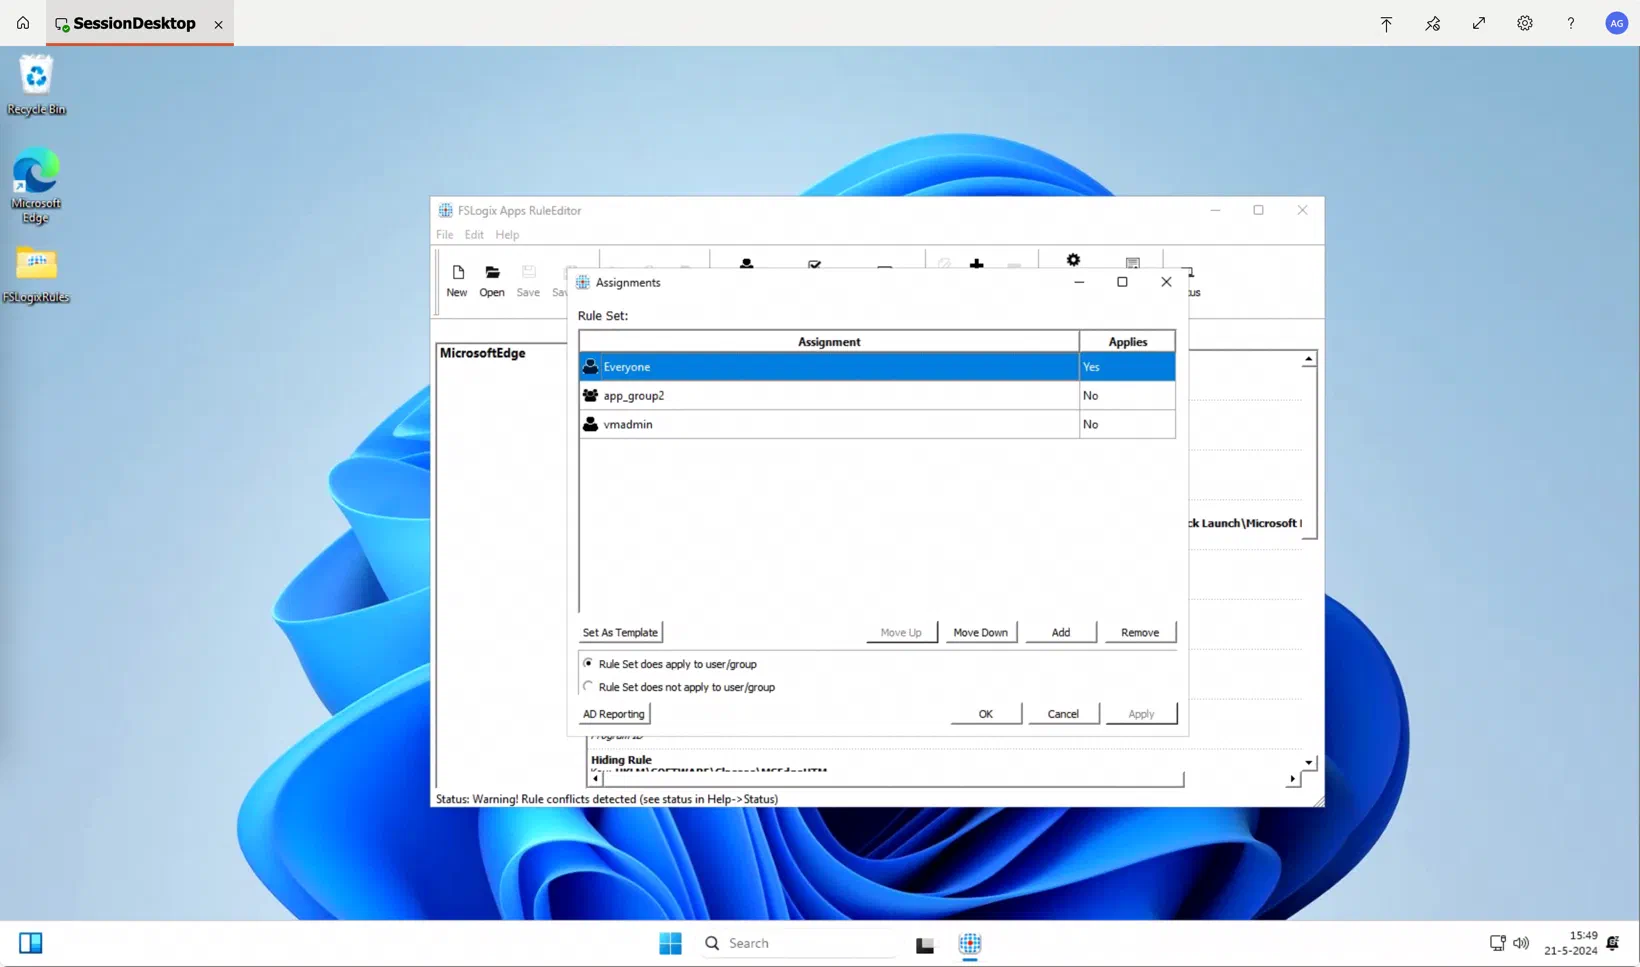
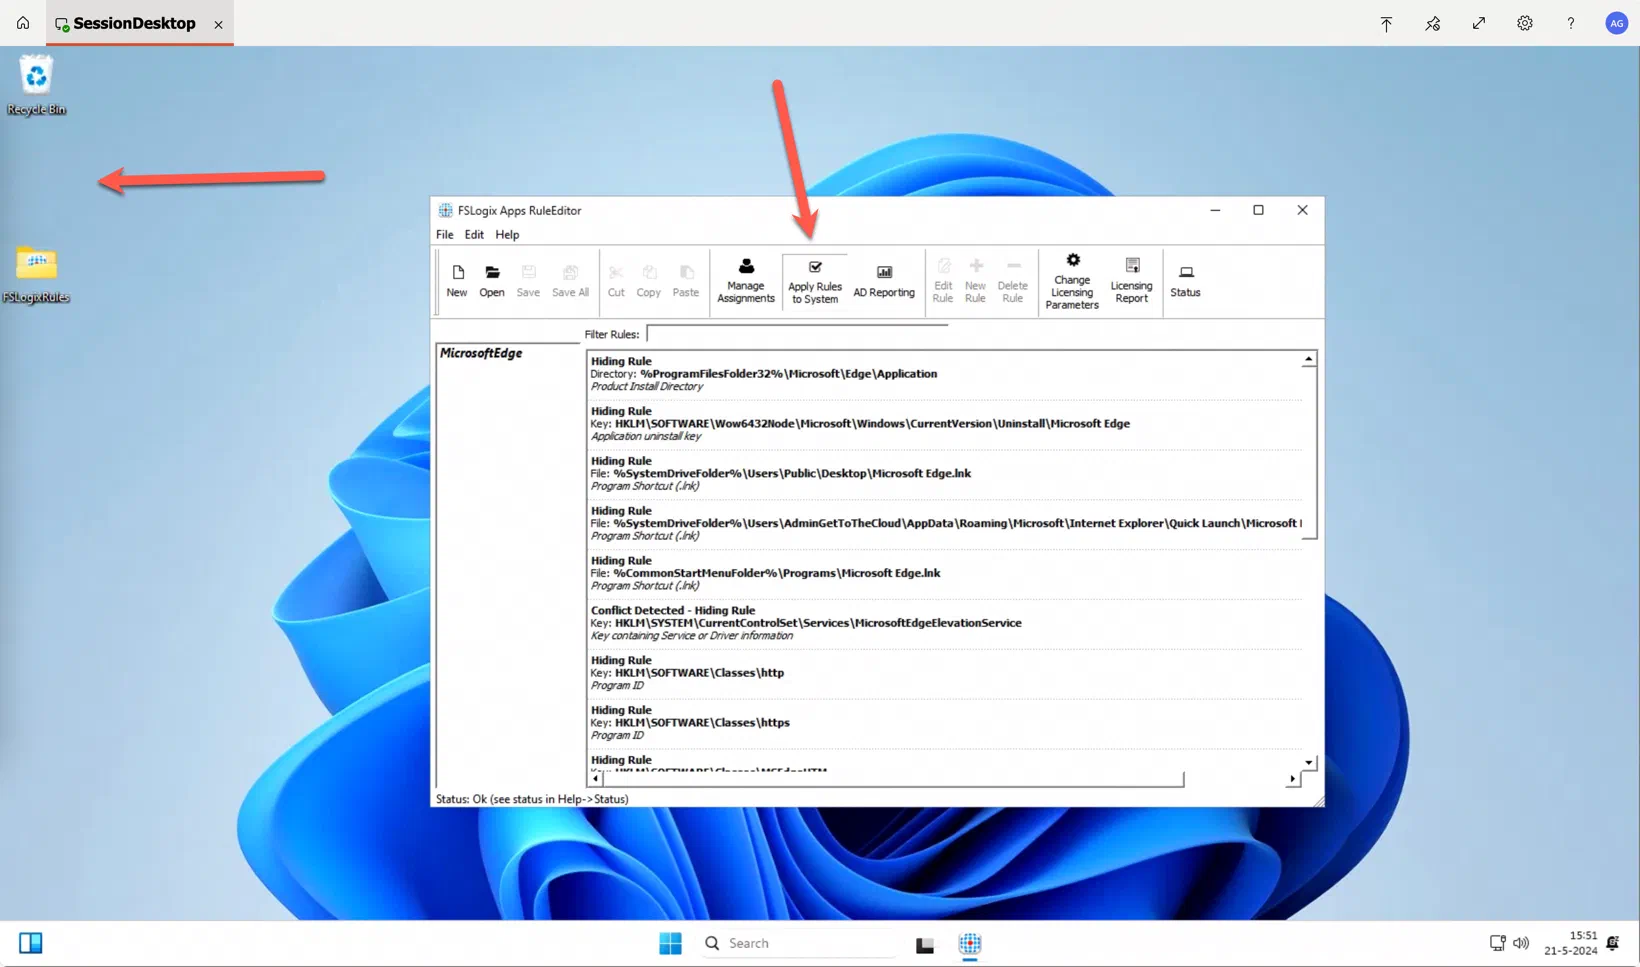
The current user is not a member of App_group2 and is also not vmadmin. If you want to test your rules and assignment you can click Apply Rules to System. You will see the Edge icon will disappear.
Now we need to upload the files to the Azure Storage Blob Container.
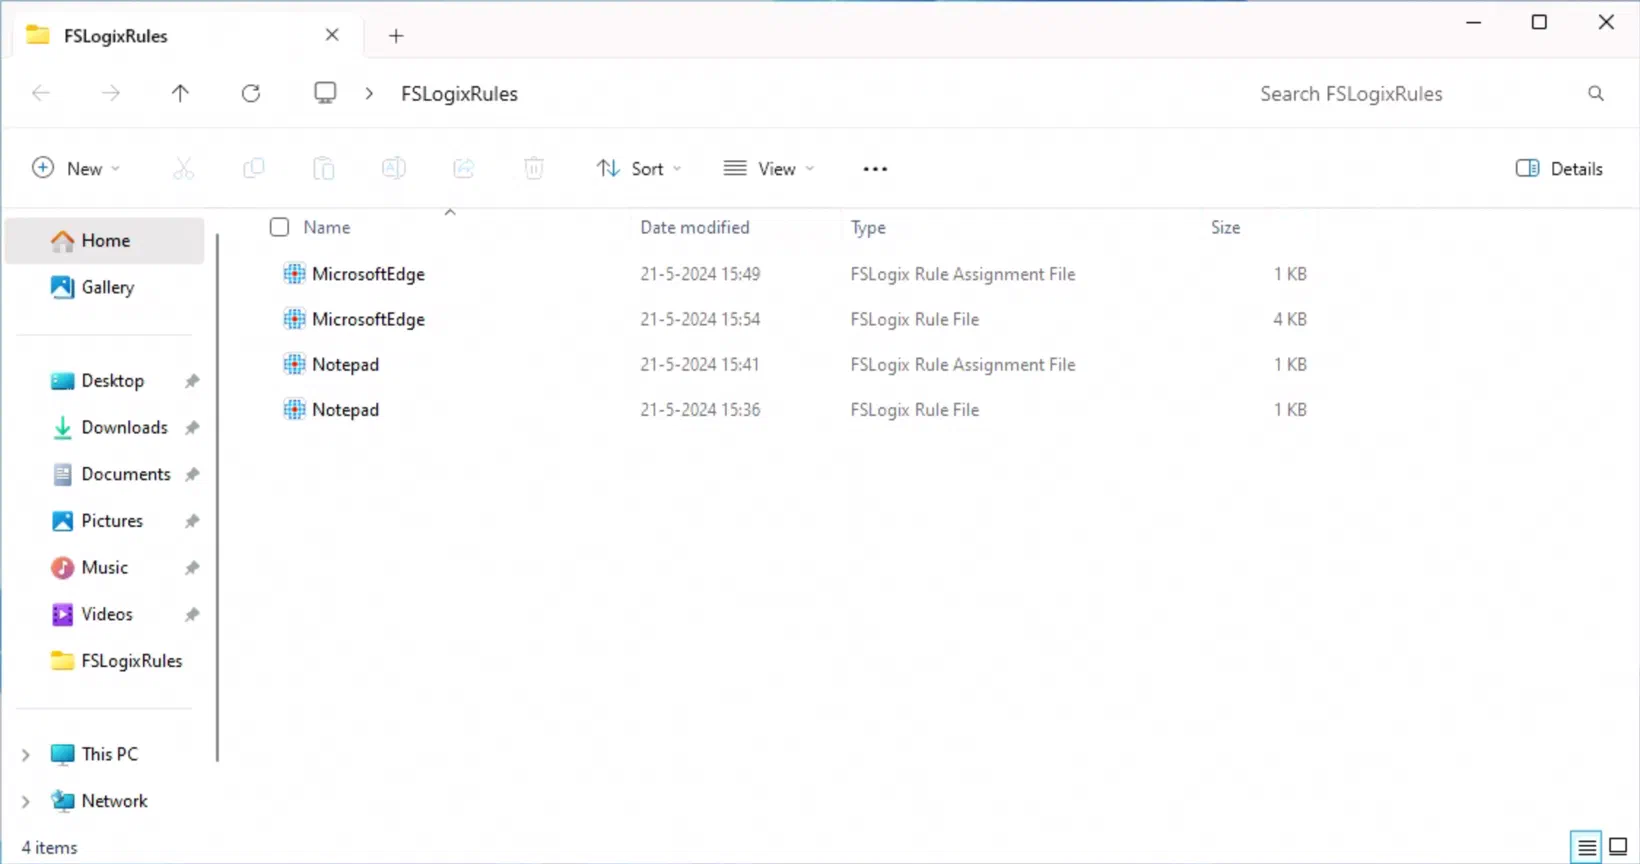
This can be done through the portal or through a drive mapping
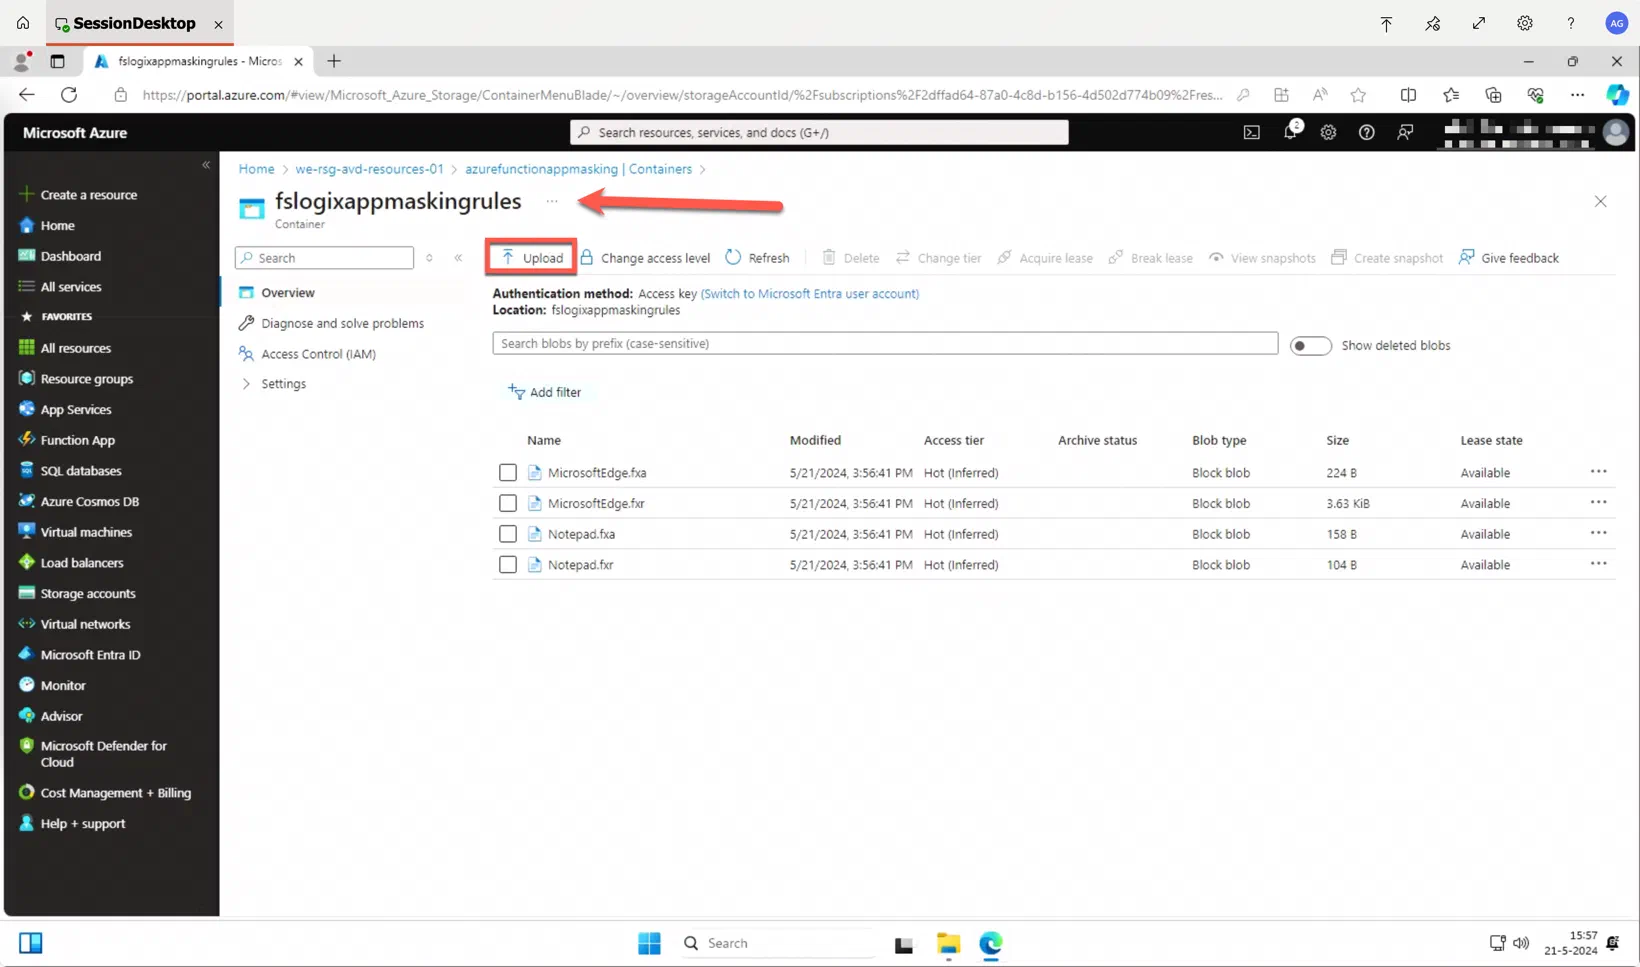
We have created a different blob for the rules.